
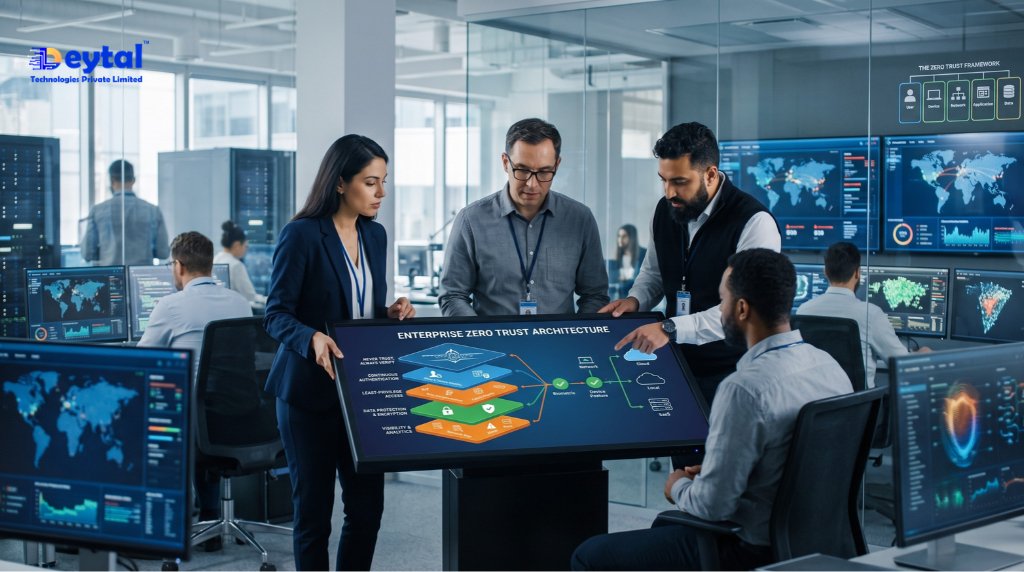
For decades, enterprise cybersecurity relied on the traditional “castle-and-moat” perimeter model. Organizations deployed firewalls and corporate VPNs to secure the corporate network edge, operating under the dangerous assumption that any user, service, or packet inside the perimeter was inherently trustworthy. In a modern computing reality defined by distributed microservices, hybrid cloud infrastructure, remote engineering teams, and sophisticated supply-chain attacks, this implicit trust model has become an enterprise liability.
Once an attacker compromises a single peripheral system or developer credential on a flat network, lateral movement is virtually unobstructed. Enterprise Zero Trust Architecture removes implicit trust from digital ecosystems entirely. Operating on the foundational mandate to “never trust, always verify,” Zero Trust enforces strict identity validation, cryptographic workload verification, micro-segmentation, and continuous risk-based telemetry for every access request—regardless of network location.
The Inherent Flaws of Perimeter-Based Security
Relying on traditional network firewalls and VPN concentrators introduces severe operational risks:
- Unfettered Lateral Movement: An attacker who breaches a low-tier service or compromises an employee endpoint can easily pivot across internal subnets to access mission-critical production databases.
- VPN Scalability and Latency Ceilings: Channelling massive distributed workforces and high-throughput microservices through centralized VPN hardware creates severe network latency and operational failure bottlenecks.
- Coarse-Grained Access Control: Traditional network security grants access at the IP or subnet layer rather than evaluating granular user identities, device posture, and individual resource contexts.
- Static Session Lifetimes: Conventional systems validate credentials once at login, ignoring real-time security events such as compromised session tokens, abnormal access patterns, or sudden geofence hops.
Castle-and-Moat Perimeter Security vs. Enterprise Zero Trust Architecture
| Security Dimension | Traditional Perimeter Model (VPN/Firewall) | Enterprise Zero Trust Architecture |
| Trust Model | Implicit trust inside internal corporate networks | Zero implicit trust; every request verified explicitly |
| Network Topology | Flat subnets with wide internal connectivity | Fine-grained micro-segmentation and ephemeral access |
| Access Verification | Validated once at network ingress (Login) | Continuously re-authenticated and contextually evaluated |
| Access Granularity | Broad network/IP-level authorization | Principle of Least Privilege (PoLP) per resource/API |
| Inspection Scope | North-south perimeter traffic only | Total inspection of north-south and east-west traffic |
| Defense Strategy | Hard outer perimeter, soft internal core | Defense-in-depth with mutual cryptographic workload identity |
Strategic Pillars for Engineering an Enterprise Zero Trust Platform
1. Cryptographic Workload Identity & Service-to-Service mTLS
Eliminate static API tokens and shared secrets across microservice backends. Engineering mutual TLS (mTLS) with short-lived cryptographic x509 certificates and SPIFFE/SPIRE workload identities via Custom Software Development Services ensures microservices strictly authenticate each other before executing cross-service data transactions.
2. Identity-Aware Web Proxies & Secure App Ingress
Replace exposed public portals and legacy VPN gateways with Identity-Aware Proxies (IAP) that validate user identity, multi-factor authentication (MFA), and endpoint device health before passing traffic to internal applications. Developing hardened, zero-trust web architectures via Website Development Services isolates internal application code from public reconnaissance and DDoS attacks.
3. Ergonomic Security Governance & Zero-Trust UI/UX Design
Security controls fail when they introduce excessive friction that drives teams toward insecure workarounds. Designing seamless single sign-on (SSO) interfaces, clear privilege-request workflows, and context-rich security prompt states through UI/UX Design Services ensures frictionless security compliance without disrupting daily engineering velocity.
4. Secure Mobile Sandboxing & Context-Aware App Endpoints
Ensure enterprise mobile applications running on unmanaged employee devices cannot leak sensitive operational data. Developing hardware-backed biometric verification, secure local enclave storage, and device health attestation runtimes via Mobile App Development Services protects data-in-transit and data-at-rest across distributed Android and iOS fleets.
5. Hardened Content Infrastructure & Technical Search Engine Trust
Protect public web platforms from injection attacks, cross-site scripting (XSS), and malicious redirects that compromise search rankings and trigger browser malware warnings. Pairing secure CMS hardening practices through WordPress Development Services with advanced SEO Services maintains top organic search authority, 100% crawl integrity, and safe Core Web Vitals delivery.
6. Trust-First Brand Authority & Enterprise Growth Funnels
Showcase enterprise security compliance, data privacy adherence (SOC 2, ISO 27001, GDPR), and zero-trust engineering standards to build buyer confidence, communicated and scaled through high-authority Digital Marketing Services.
Build Resilient Zero-Trust Infrastructure with Deytal Technologies
Migrating an enterprise from legacy network perimeters to a zero-trust architecture requires a strategic overhaul of identity providers, network segmentation, and API gateway policies. Deytal Technologies Pvt. Ltd. designs, audits, and builds production-grade zero-trust systems, microservice identity layers, and secure cloud web platforms engineered for maximum compliance, speed, and defense-in-depth protection.
Frequently Asked Questions (FAQ)
Q1: What are the primary core tenets of the NIST Zero Trust Architecture (SP 800-207)?
NIST SP 800-207 defines several fundamental principles: all data sources and computing services are considered resources; all communication is secured regardless of network location; access to individual enterprise resources is granted on a per-session basis; and resource access is dynamically determined by policy, including client identity, device health, and environmental attributes.
Q2: How does micro-segmentation prevent lateral attack movement?
Micro-segmentation divides an infrastructure environment into distinct, isolated security segments down to the individual workload level. By enforcing granular firewall rules and software-defined network policies between individual containers, VMs, and databases, an attacker who compromises a front-end server is strictly blocked from communicating with adjacent internal services or backend ledgers.
Q3: Does implementing Zero Trust degrade web application performance?
When engineered properly, Zero Trust actually improves performance. Modern implementations utilize lightweight, distributed Identity-Aware Proxies and edge termination nodes rather than hair-pinning all global traffic through slow, centralized corporate VPN hardware. Workload identity checks and cryptographic validations execute within sub-millisecond ranges using optimized local proxies and connection-reuse connection pooling.
